Security
Keep each patient's records inside your organization
Referrals, results and visit notes are some of the most sensitive records a doctor holds. Here are the controls we apply today, with no claims we cannot back.
Controls
Check the defaults every account gets
Keep one account per organization
A practice or hospital team works in its own account. Patient workspaces belong to that account and never appear in another.
We check sharing permissions on the server
You share a workspace or a document as viewer or editor. We check that permission on the server on every request, not only in the interface.
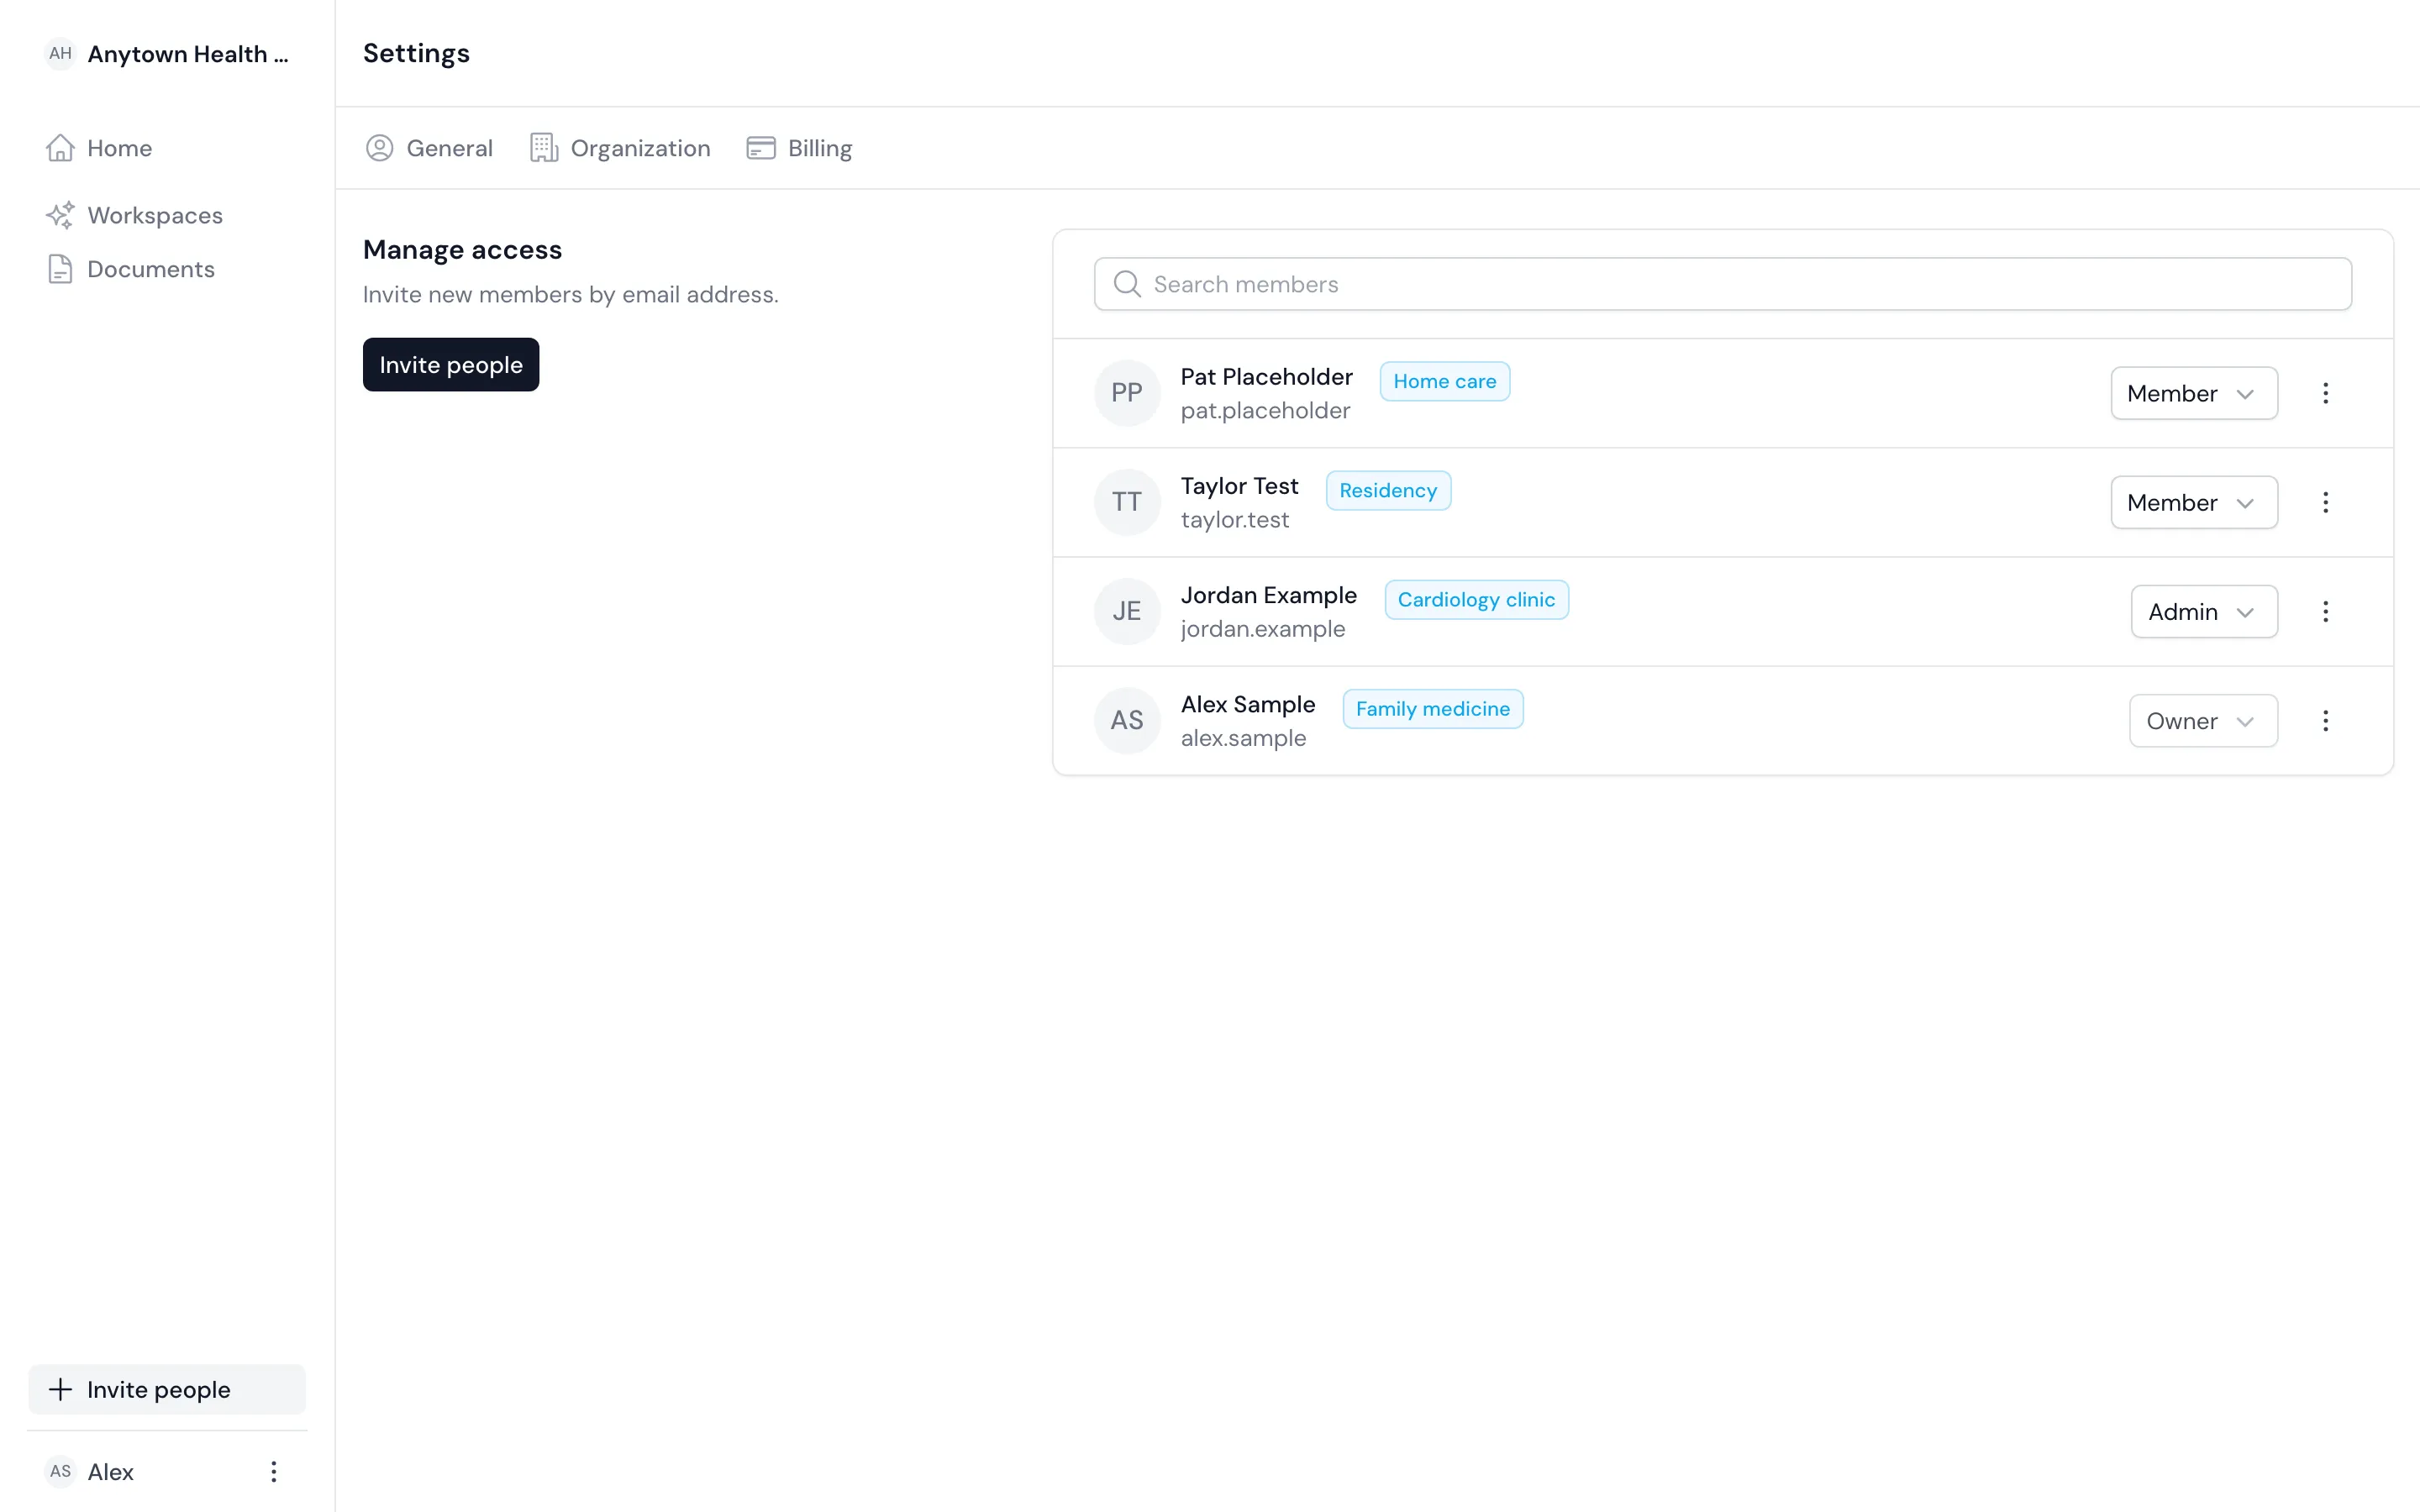
Give every member a role
Each member has an owner, admin or member role. Owners and admins decide who belongs to the account.
Control how your organization signs in
Members sign in with an email link or a password, and organizations can use single sign-on with SAML.
Connect over HTTPS only
We serve the website and the app over HTTPS only.
Ask us to delete your data
Write to us and we delete your organization's workspaces, sources and documents.
Patient data
Add identifiable patient data only under an agreement
Your organization decides what goes in and stays the controller of it. We process it only to run the service for you.
You sign the agreement first
Sign a data processing agreement for your jurisdiction before you add identifiable data.
We do not train on patient data
We do not use what you upload to train AI models.
You edit every draft
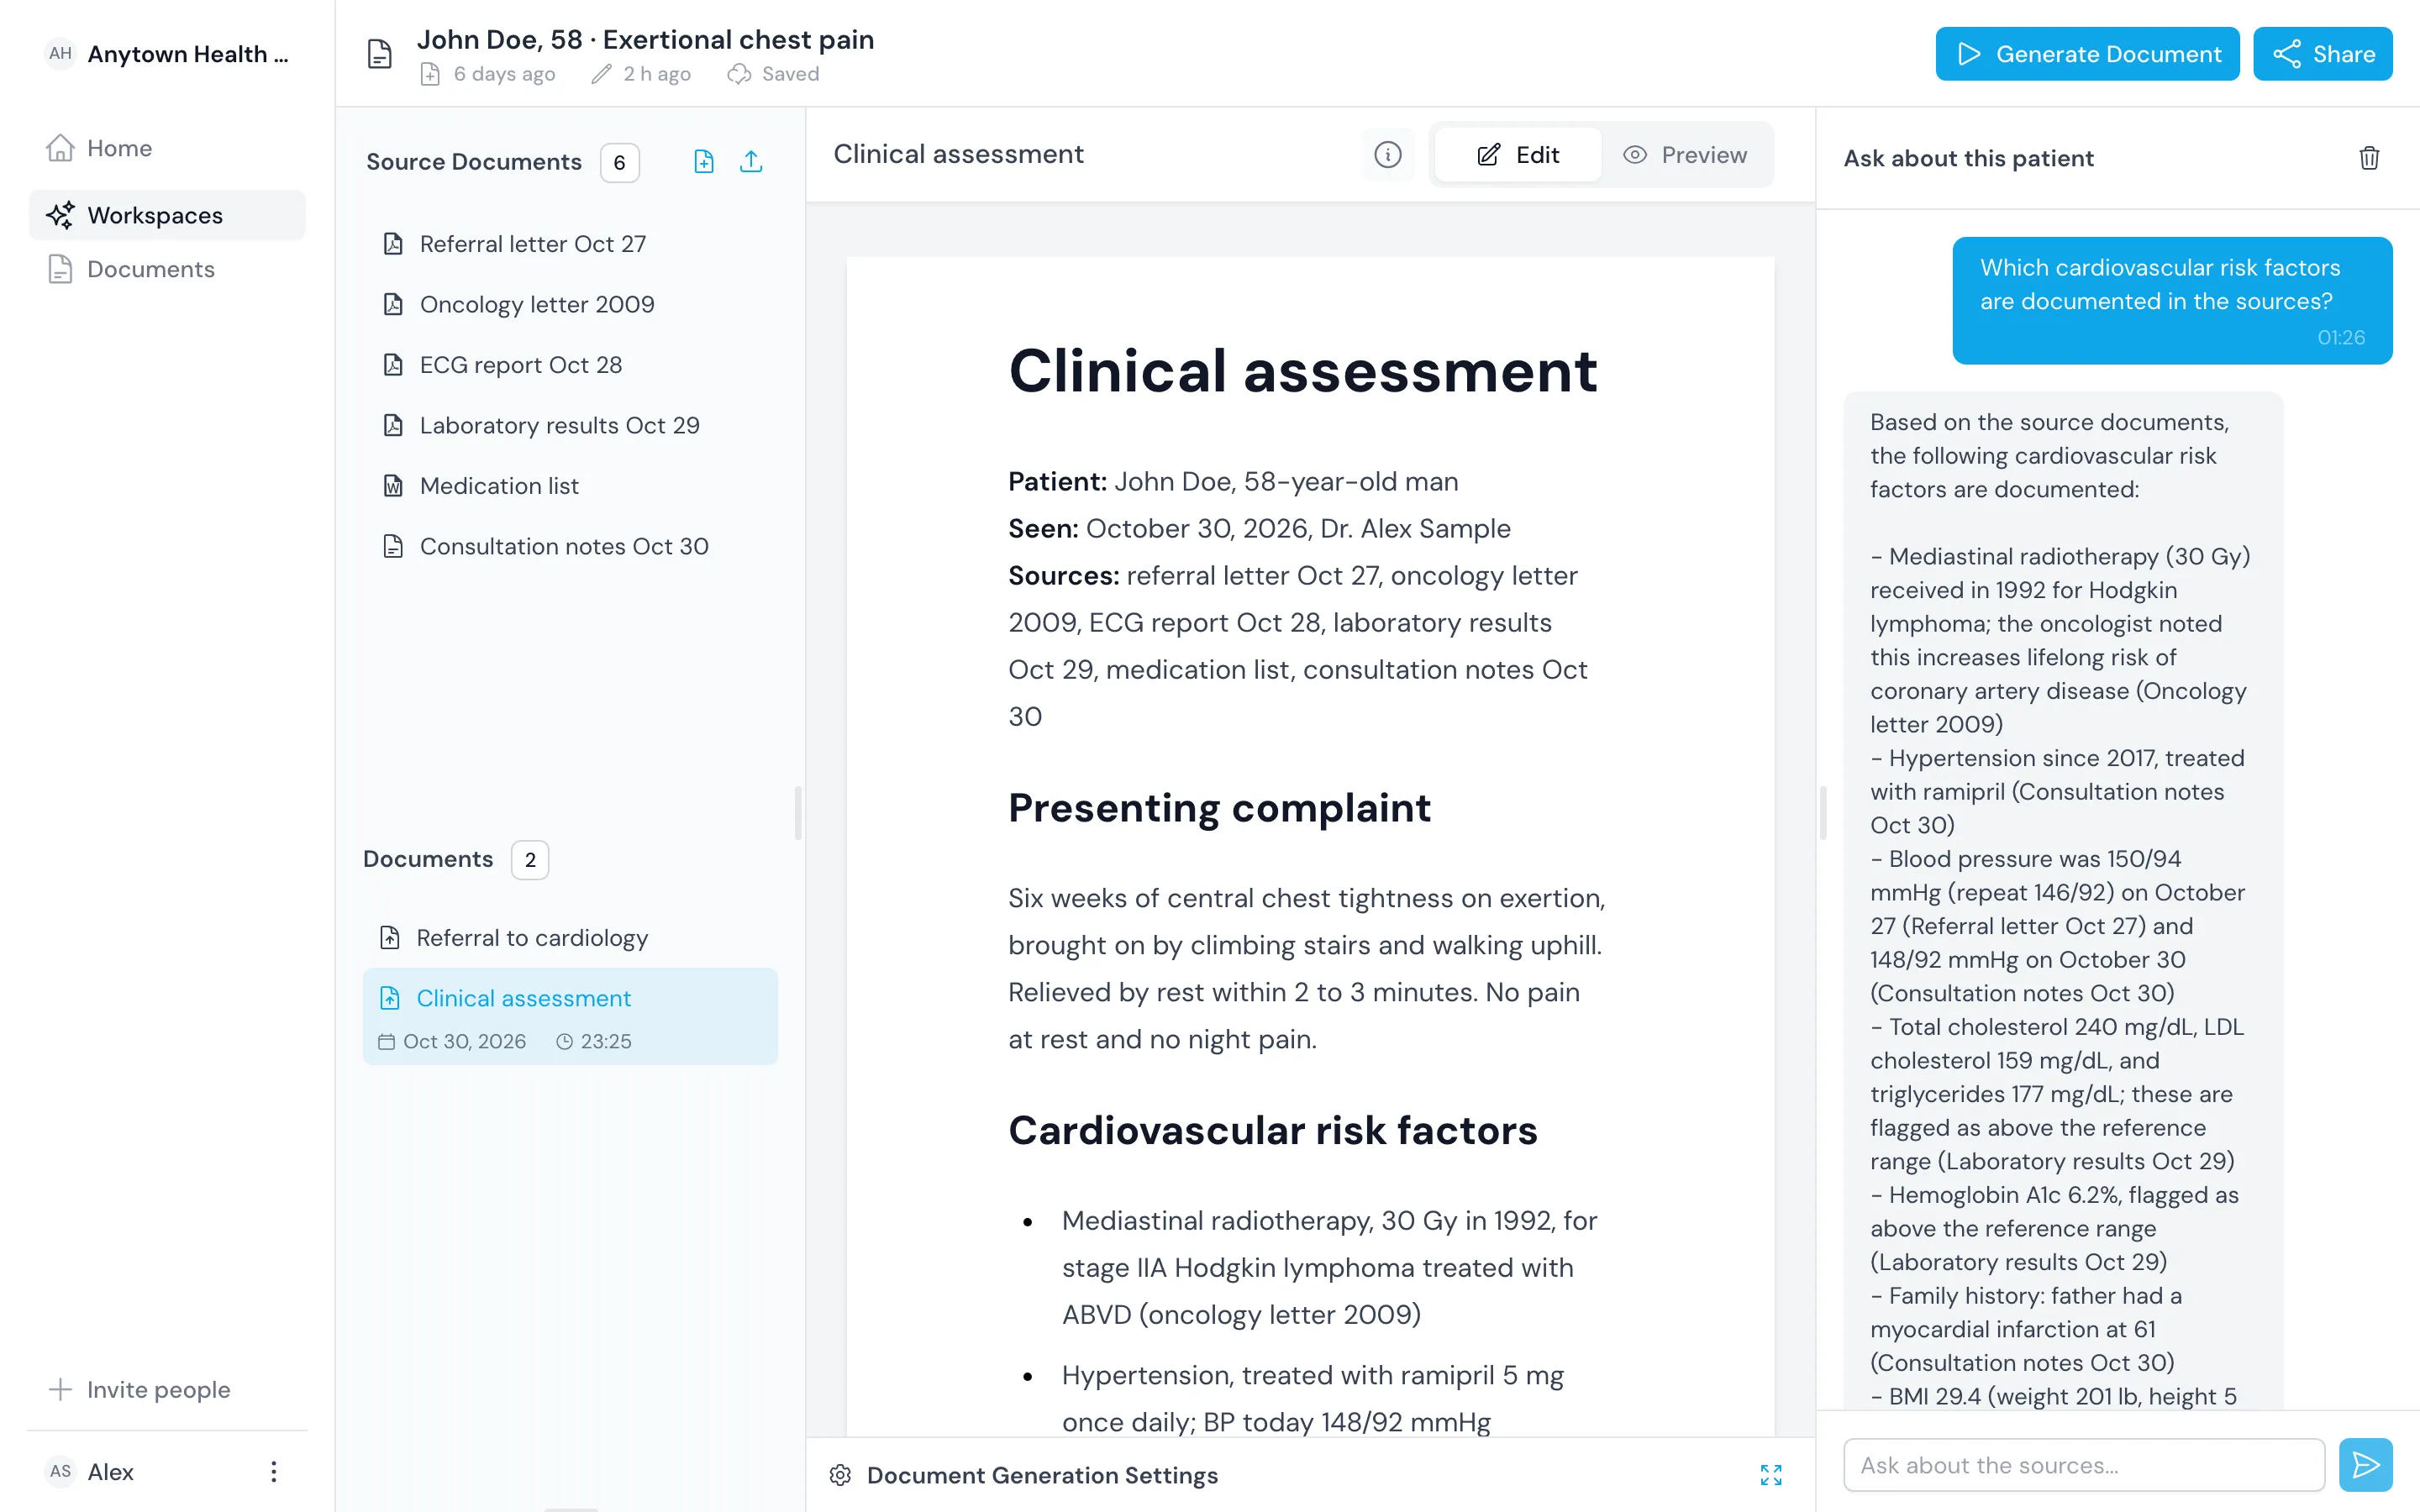
Nothing reaches a record until a doctor has edited and exported it.
Documents
Find the paperwork your reviewers will ask for
Ask for anything not listed here at hello@workupdesk.com.
- Privacy policyWhat the website and waitlist collect, and how the product will handle patient data
- Terms of serviceThe terms for using the product, including clinical responsibility
- Data processing agreementWe agree it with your organization before you add identifiable patient data
Questions
Frequently asked questions
Do you hold a security certification?
Not yet, and this page will not claim one before it is true. We make no claim of HIPAA or GDPR compliance here. The controls on this page describe how the product works today.
Who can see a patient's workspace?
The colleagues you share it with, as viewers or editors, within your organization's account. We check that permission on the server on every request.
Is patient data used to train models?
No. We do not use patient data to train AI models. The data processing agreement names the AI providers that process it and the terms they work under.
When can we add real patient data?
Once a data processing agreement for your jurisdiction is in place with us. Until then, use de-identified or made-up cases.
How do we delete our data?
Write to us and we delete your organization's workspaces, sources and documents.